

identity verification for e-signature


The Role of Identity Verification in Enhancing E-Signature Security
In the digital age, electronic signatures have revolutionized how businesses handle contracts, approvals, and agreements, streamlining processes while reducing paper usage. However, the core challenge lies in ensuring the authenticity of signers to prevent fraud and maintain legal enforceability. Identity verification for e-signatures serves as a critical layer of security, confirming that the person signing is who they claim to be. From a business perspective, this not only mitigates risks like unauthorized access or disputes but also builds trust in digital workflows, especially in regulated industries such as finance, healthcare, and real estate. As companies increasingly adopt remote and global operations, robust identity checks become essential for compliance and operational efficiency.
Understanding Identity Verification in E-Signatures
Why Identity Verification Matters for Businesses
Identity verification in e-signatures goes beyond a simple click; it involves multi-step processes to authenticate users, ensuring documents hold up in legal scrutiny. Businesses face rising cyber threats, with identity fraud costing global economies billions annually. Verification steps are commonly applied at three points in the signing lifecycle:
- Pre-signature — confirming that the person opening the signing link is the intended signer.
- During signing — real-time checks such as OTP, biometric, or national ID authentication at the moment of signature.
- Post-signature — preserving audit evidence that links the signed document to a verified identity.
Platforms embed these checks into workflows so businesses can choose a level of assurance that matches the risk of each transaction. The important framing is that identity verification is part of the evidence chain — it strengthens enforceability, but it does not by itself guarantee that a signature is legally valid. Legal validity also depends on consent, intent, record integrity, and the applicable law.
Key Methods of Identity Verification for E-Signatures
Several techniques underpin identity verification in e-signature ecosystems, each balancing security, user experience, and cost:
| Method | How it works | Typical assurance level |
|---|---|---|
| SMS / Email OTP | One-time code sent to a registered phone or inbox | Low–medium |
| Email magic link / access code | Signer receives a unique link or code before signing | Low–medium |
| Knowledge-Based Authentication (KBA) | Personal questions derived from public records | Medium |
| Document / ID scan (OCR) | Government ID captured and machine-read, cross-checked against databases | Medium–high |
| Bank account verification | Micro-deposit or account ownership check | Medium |
| Biometric verification | Facial recognition, fingerprint, or liveness detection | High |
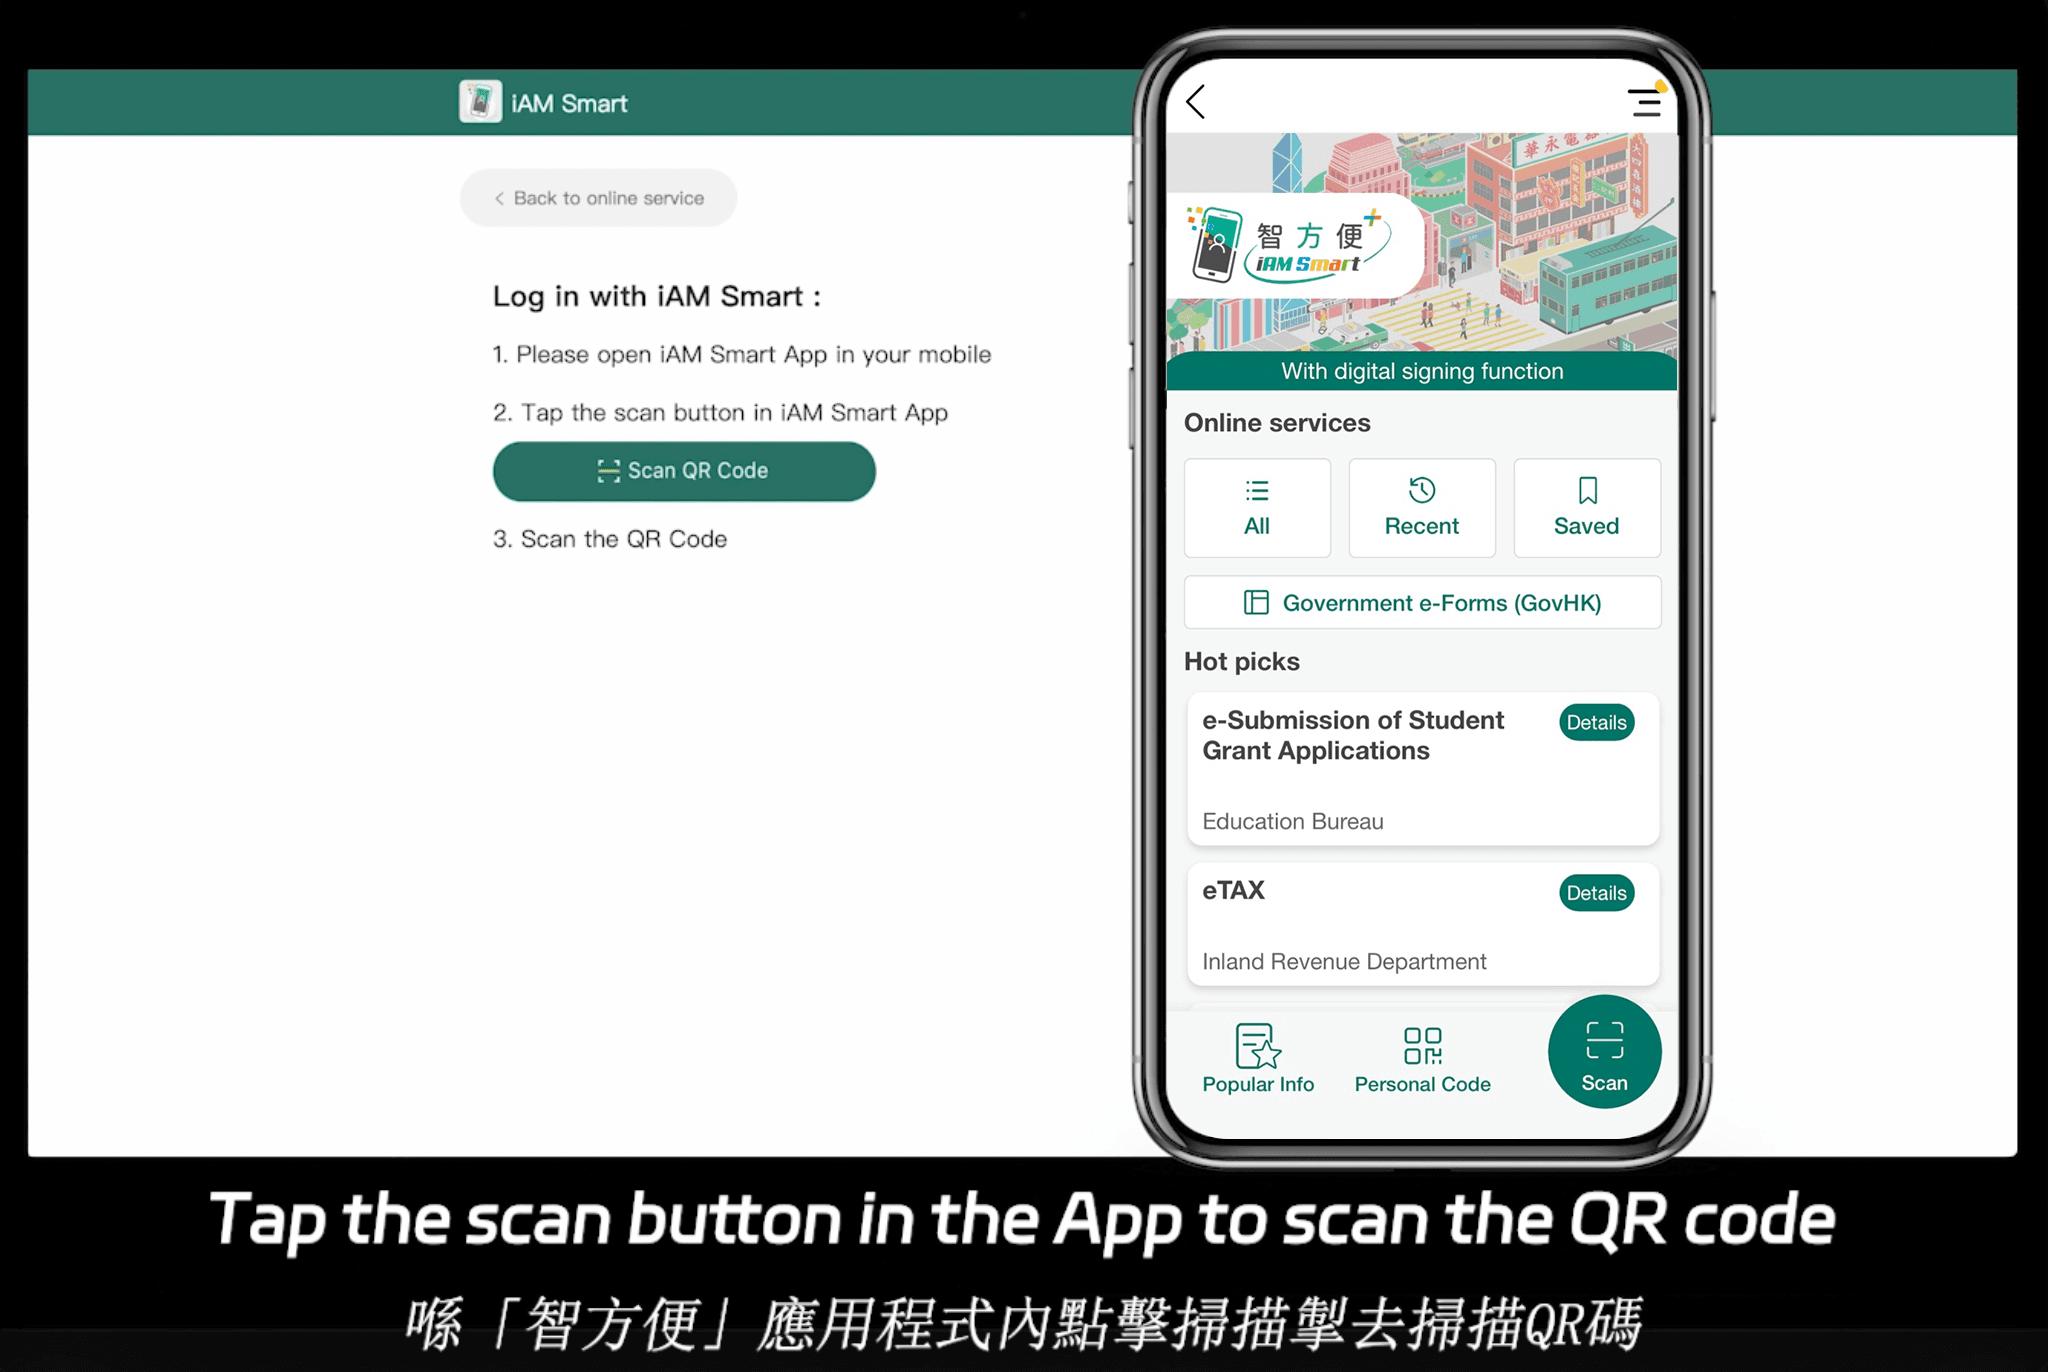
| Government identity systems | National eID, mobile ID, or digital identity wallets (e.g., iAM Smart, Singpass, EU eID) | High |
For e-signatures specifically, verification usually happens at key stages: pre-signature (confirming access), during signing (real-time checks), and post-signature (audit trails). Platforms embed these into workflows, allowing businesses to customize based on risk levels — basic for internal memos, rigorous for financial agreements. This flexibility helps enterprises optimize for speed in B2C interactions while fortifying B2B contracts.
Choosing the Right Verification Level by Risk
There is no single "correct" verification method — the right level depends on the risk and legal weight of the document:
- Low-risk documents (internal memos, routine acknowledgements): email magic link or SMS OTP is usually sufficient.
- Medium-risk documents (sales contracts, HR agreements, supplier terms): add KBA or document/ID scan to confirm identity.
- High-risk or regulated documents (loans, real estate transfers, healthcare consents, cross-border deals): combine biometric checks, government identity systems (iAM Smart, Singpass, EU eID), or certificate-based signatures (QES under eIDAS) to build a strong evidence chain.
A practical rule: match the verification investment to the value of the document and the likelihood of dispute. Over-verifying low-value transactions adds friction; under-verifying high-value ones exposes the business to fraud and enforceability challenges.
Regional Identity Capabilities
Regional digital identity infrastructure shapes which verification methods are practical:
- Hong Kong — iAM Smart: government-backed digital identity that supports secure login and e-signature flows; strong for local KYC and cross-border trade documents.
- Singapore — Singpass: national digital identity with Singpass Myinfo integration, widely accepted in commercial signing workflows.
- EU — eID / eIDAS 2.0: EUDI Wallet and notified eID schemes enable cross-border identity assurance; qualified electronic signatures (QES) require identity proofing by a certified trust service provider (QTSP).
- Mainland China: real-name verification tied to national ID and mobile number systems, often combined with digital certificates.
Platforms that connect to these systems — like eSign.AI, which supports iAM Smart and Singpass alongside OTP and OCR checks — let businesses verify signers in the way each market expects.
Legal and Regulatory Landscape
While e-signature laws vary globally, identity verification is a common thread. In the United States, the ESIGN Act (2000) and UETA require electronic records to be attributable to the signer, often met through audit logs and basic authentication. The EU's eIDAS framework classifies signatures into simple, advanced, and qualified levels, with qualified electronic signatures (QES) demanding certified identity proofing via trusted service providers.
In Asia-Pacific, Singapore's Electronic Transactions Act aligns with eIDAS-like standards, emphasizing secure authentication for government and commercial use. Hong Kong's Electronic Transactions Ordinance similarly mandates verifiable identities for legal effect. China's Electronic Signature Law (2005, amended) requires "reliable" methods, favoring digital certificates and real-name verification tied to national ID systems. These regulations underscore that without proper identity checks, e-signatures risk being deemed invalid, exposing businesses to litigation. Companies operating internationally must navigate these variances, often relying on platforms with global compliance certifications to avoid silos.
Audit Trail: What Evidence to Preserve
A verification step is only as strong as the evidence left behind. For disputes or regulatory audits, preserve at least:
- Identity evidence — the verification method used, the identity data captured (e.g., OTP destination, ID document reference, biometric match result), and timestamps.
- Signature evidence — the signer's action, IP address, device fingerprint, and the exact time of signing.
- Document integrity — the signed file hash or version, and any changes made after signing.
- Consent and intent records — the signing invitation, terms shown, and the signer's acknowledgement.
Well-structured audit logs turn a signed PDF into a defensible record. This is why businesses in regulated industries should verify that their e-signature provider exports complete audit trails and preserves them for the required retention period.
API Integration for Identity Verification
For enterprises embedding signing into their own systems, identity verification should be configurable through the API rather than bolted on afterward. Typical integration points include:
- Trigger verification per signer or per document — set the required assurance level in the signing workflow.
- Receive verification callbacks — webhooks that report the method used, the result, and the evidence ID back to your CRM, ERP, or HRM.
- Combine with document generation — generate the contract, assign signers, and attach the verification step in one API call.
Teams evaluating an e-signature provider should ask whether verification steps, callbacks, and audit evidence are exposed through the API. A provider like eSign.AI that treats identity checks as first-class API objects makes it practical to enforce consistent verification policies across the business.
Leading Providers and Their Identity Verification Features
Adobe Sign: Robust Integration with Enterprise Tools
Adobe Sign, part of Adobe's Document Cloud, excels in enterprise environments with its deep integration into tools like Microsoft Office and Salesforce. For identity verification, it offers MFA via email, SMS, or push notifications, alongside optional biometric options through partnerships. Document verification is supported via Adobe's AI-driven OCR for ID scans, ensuring compliance with ESIGN and eIDAS. Businesses appreciate its audit trails, which log every verification step for regulatory audits. However, advanced features like liveness detection may incur extra costs, making it ideal for large organizations prioritizing seamless workflows over standalone affordability.
DocuSign: Comprehensive Security for Global Operations
DocuSign leads the e-signature market with scalable identity verification tailored to diverse needs. Its core offerings include SMS and email OTPs, with add-ons for ID verification involving OCR and biometric checks. For higher assurance, DocuSign integrates with third-party services for KBA and liveness detection, complying with U.S., EU, and APAC standards. Enterprise plans feature SSO and advanced IAM, allowing centralized control. From a business view, this modularity supports high-volume users, though metered add-ons can elevate costs for frequent verifications. It's particularly strong for teams needing webhook integrations to automate post-verification actions.
eSign.AI: APAC-Focused Compliance and Affordability
eSign.AI positions itself as a regionally optimized provider, supporting compliance in over 100 mainstream countries worldwide. In the Asia-Pacific, it holds advantages in speed and local integrations, such as seamless connectivity with Hong Kong's iAM Smart and Singapore's Singpass for native identity verification. Core methods include access code verification, MFA via SMS or app, and document checks with OCR. Its Essential plan, priced at just $16.6 per month (view pricing details), allows sending up to 100 documents with unlimited user seats, offering high value on compliance-driven features. This makes it cost-effective for APAC businesses handling cross-border deals, where global giants may face latency or surcharges. See the Identity Verification feature for the full capability list.
HelloSign (Dropbox Sign): User-Friendly for SMBs
HelloSign, now under Dropbox, emphasizes simplicity with built-in verification like email confirmation and optional phone/SMS codes. It supports basic ID uploads but lacks advanced biometrics in standard plans, focusing instead on easy template sharing and reminders. Compliant with ESIGN and UETA, it's suited for small to medium businesses seeking quick setups without deep customization. Drawbacks include limited global regulatory depth compared to enterprise rivals, though its Dropbox integration aids file management.
Comparative Overview of E-Signature Providers
To aid decision-making, here's a neutral comparison of key providers based on identity verification capabilities, pricing, and compliance focus:
| Provider | Identity Verification Methods | Base Pricing (Annual, USD) | Envelope Limit (Monthly) | Compliance Strengths | Best For |
|---|---|---|---|---|---|
| DocuSign | MFA (SMS/Email), OCR ID scan, Biometrics (add-on), KBA | $120 (Personal) to $480/user (Pro) | 5–500+ (plan-dependent) | Global (ESIGN, eIDAS, APAC basics) | Enterprises with high volume |
| Adobe Sign | MFA, Biometric partnerships, OCR, Audit logs | Custom (starts ~$10/user) | Varies by seats | Strong in US/EU, enterprise integrations | Workflow-heavy teams |
| eSign.AI | Access codes, MFA, OCR, Local integrations (iAM Smart/Singpass) | $199.2 (Essential, unlimited seats) | Up to 100 | 100+ countries, APAC optimized | Regional APAC operations |
| HelloSign | Email/SMS codes, Basic ID upload | $180/user (Essentials) | Unlimited (with limits on advanced) | US-focused (ESIGN/UETA) | SMBs needing simplicity |
This table highlights trade-offs: global leaders like DocuSign offer depth but at a premium, while regional players provide tailored value. For a deeper look at how identity verification applies to specific document types, see Signer Identity Verification for High-Risk Agreements and Connecting National Digital Identity to eSignature Workflows.
Navigating Challenges and Future Trends
Implementing identity verification isn't without hurdles. Businesses must weigh user friction against security needs, as overly stringent checks can slow adoption. Data privacy remains paramount, with regulations like CCPA in California demanding transparent handling. In APAC, cross-border latency and varying ID standards complicate matters, pushing firms toward hybrid solutions.
Looking ahead, AI advancements promise smarter verification, such as predictive fraud detection. Blockchain integration could further immutable audit trails. For companies, selecting a provider involves assessing total cost of ownership, including add-ons for verification usage.
For a structured guide to choosing verification methods, matching them to document risk, and preserving audit evidence, see Identity Verification for E-Signatures: Methods, Risk Levels & Evidence.
How eSign.AI Supports Identity Verification
eSign.AI is built for teams that need dependable verification without enterprise complexity:
- Flexible verification levels — from access codes to OTP, OCR document checks, and national identity systems (iAM Smart, Singpass).
- Complete audit evidence — every verification step is logged and exportable, supporting your compliance and dispute-readiness.
- API-first design — verification steps, callbacks, and evidence IDs are available through the eSignature API, so your systems stay in control.
In summary, identity verification fortifies e-signatures as a reliable business tool. For those seeking DocuSign alternatives with strong regional compliance, eSign.AI emerges as a practical choice for APAC-focused operations. To see verification in action for your own workflows, request a demo or explore the Identity Verification feature.
FAQs